Anything2Shell.com: Free Visibility, Alerts & Mitigations for Rapidly Evolving *2Shell RCE Attacks
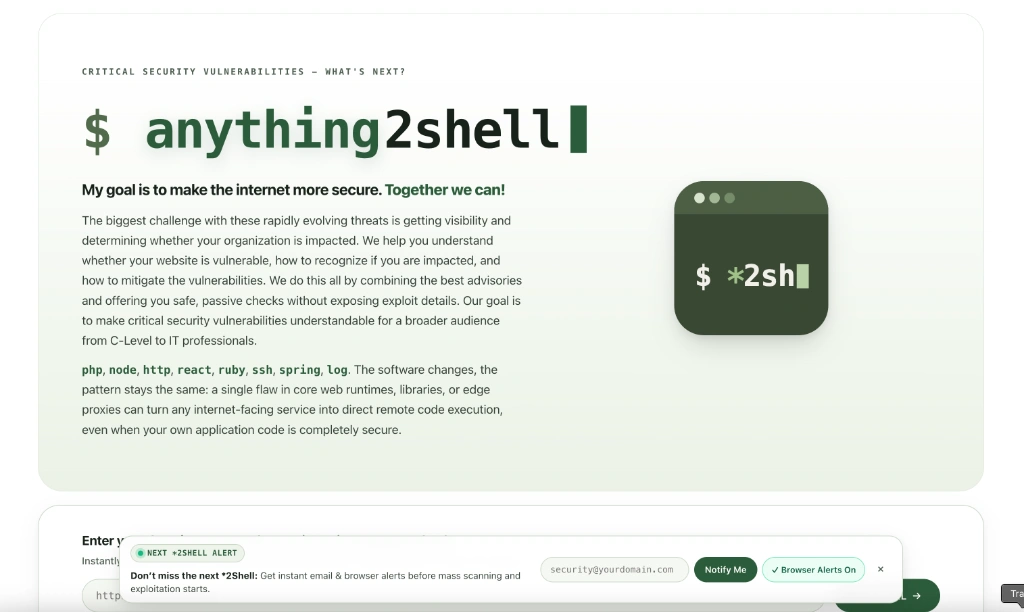
From Log4Shell and Spring4Shell to the recent PHP2Shell emergency, the software name keeps changing—php, node, http, react, ruby, ssh, spring, log—but the pattern stays the same: a single flaw in a core web runtime, library, or edge proxy can expose any internet-facing service to unauthenticated Remote Code Execution (RCE), even when your own application code is completely secure.
With AI-assisted vulnerability research compressing exploit timelines from months into days, the hardest question in the first hours of a disclosure is always the same: Are we impacted right now, and what do we do first?
That is why anything2shell.com was built—a 100% free community resource designed for both CISOs and IT & Security Professionals, with one simple goal: to make the internet a more secure place.
What You Can Do on Anything2Shell.com
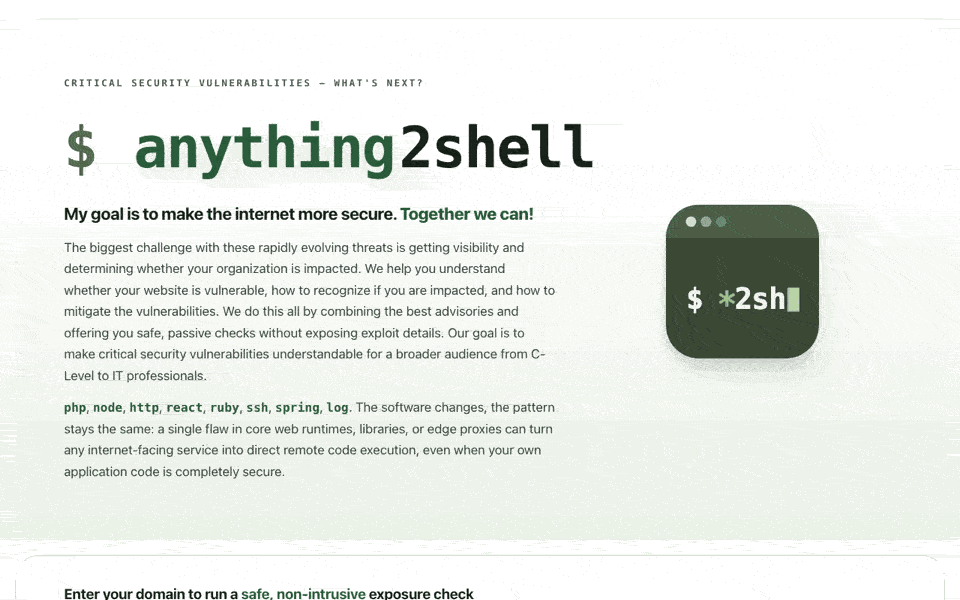
Whether you are an engineer triaging production servers at 2:00 AM or a CISO preparing an executive update before mass scanning begins, anything2shell.com gives you four immediate capabilities in one place:
- Scan Your Website for Impact (Safe & Non-Intrusive): Enter your domain to run a safe, passive exposure check—giving you direct visibility into whether your internet-facing services are vulnerable without firing active exploit payloads.
- Get Instant
*2Shell& IoC Notifications: Subscribe via email or browser alerts so you are notified the moment a new*2ShellRCE vulnerability is discovered—and whenever there are rapid changes in Indicators of Compromise (IoCs), mass-scanning activity, or upstream advisories. - Apply Proven Mitigations Across Runtimes:
Cut through fragmented advisories with clear, actionable remediation steps showing how to patch, contain, and fix different
*2Shellvulnerabilities across web runtimes, OS packages, and edge protections. - Get Risk Insights with the Boardroom Reference Card: Translate deeply technical CVEs into clear business impact in seconds. Use the built-in Boardroom Reference Card to walk into leadership meetings prepared as a CISO—or to brief your CISO clearly and concisely when every minute counts.
Free for Everyone — Together We Can Make the Internet Safer
There is no paywall, no upsell, and no product pitch behind anything2shell.com. It is a free community service built to close the visibility gap between initial vulnerability disclosure and practical defense—from the terminal all the way to the boardroom.
Try a safe check on your domain or enable alerts for the next wave at https://anything2shell.com/. Together, let’s make the internet a more secure place! 🛡️
Jorge Liauw Calo
Security Engineer at Google Cloud (Google Cybershield) with 13+ years of experience in Cybersecurity across highly regulated industries including Semiconductor, Banking, Fintech, and Insurance. Active member of the Google Cloud Community BeNeLux and Google Cloud Security Community Amsterdam.